Setting up and using limits
Limits restrict the Smart Monitor resources available for query processing. The system supports default values and separate configurations for roles and users.
Setting up user and role limits
For each field, the system first checks the user’s personal value. If the value is absent, the system considers the user’s roles with limit configurations. A missing field in an existing role configuration uses the default value; roles without a limit configuration are excluded from the calculation. Numeric parameters use the largest value, while command lists are combined without duplicates. If no personal or role value is available, the default limit applies.
Open Main Menu - Settings - Module Settings - Limits. The page provides default, role and user limit configurations. To find a configuration, enter the role or user name in the search field.
Editor parameters are divided into three groups:
Search- search interval, running time, parallel request count and source record countPipeline- document count and data size between commands, and maximum lookup sizeBackground results- result retention time and disk quota
The list of allowed commands is configured separately.
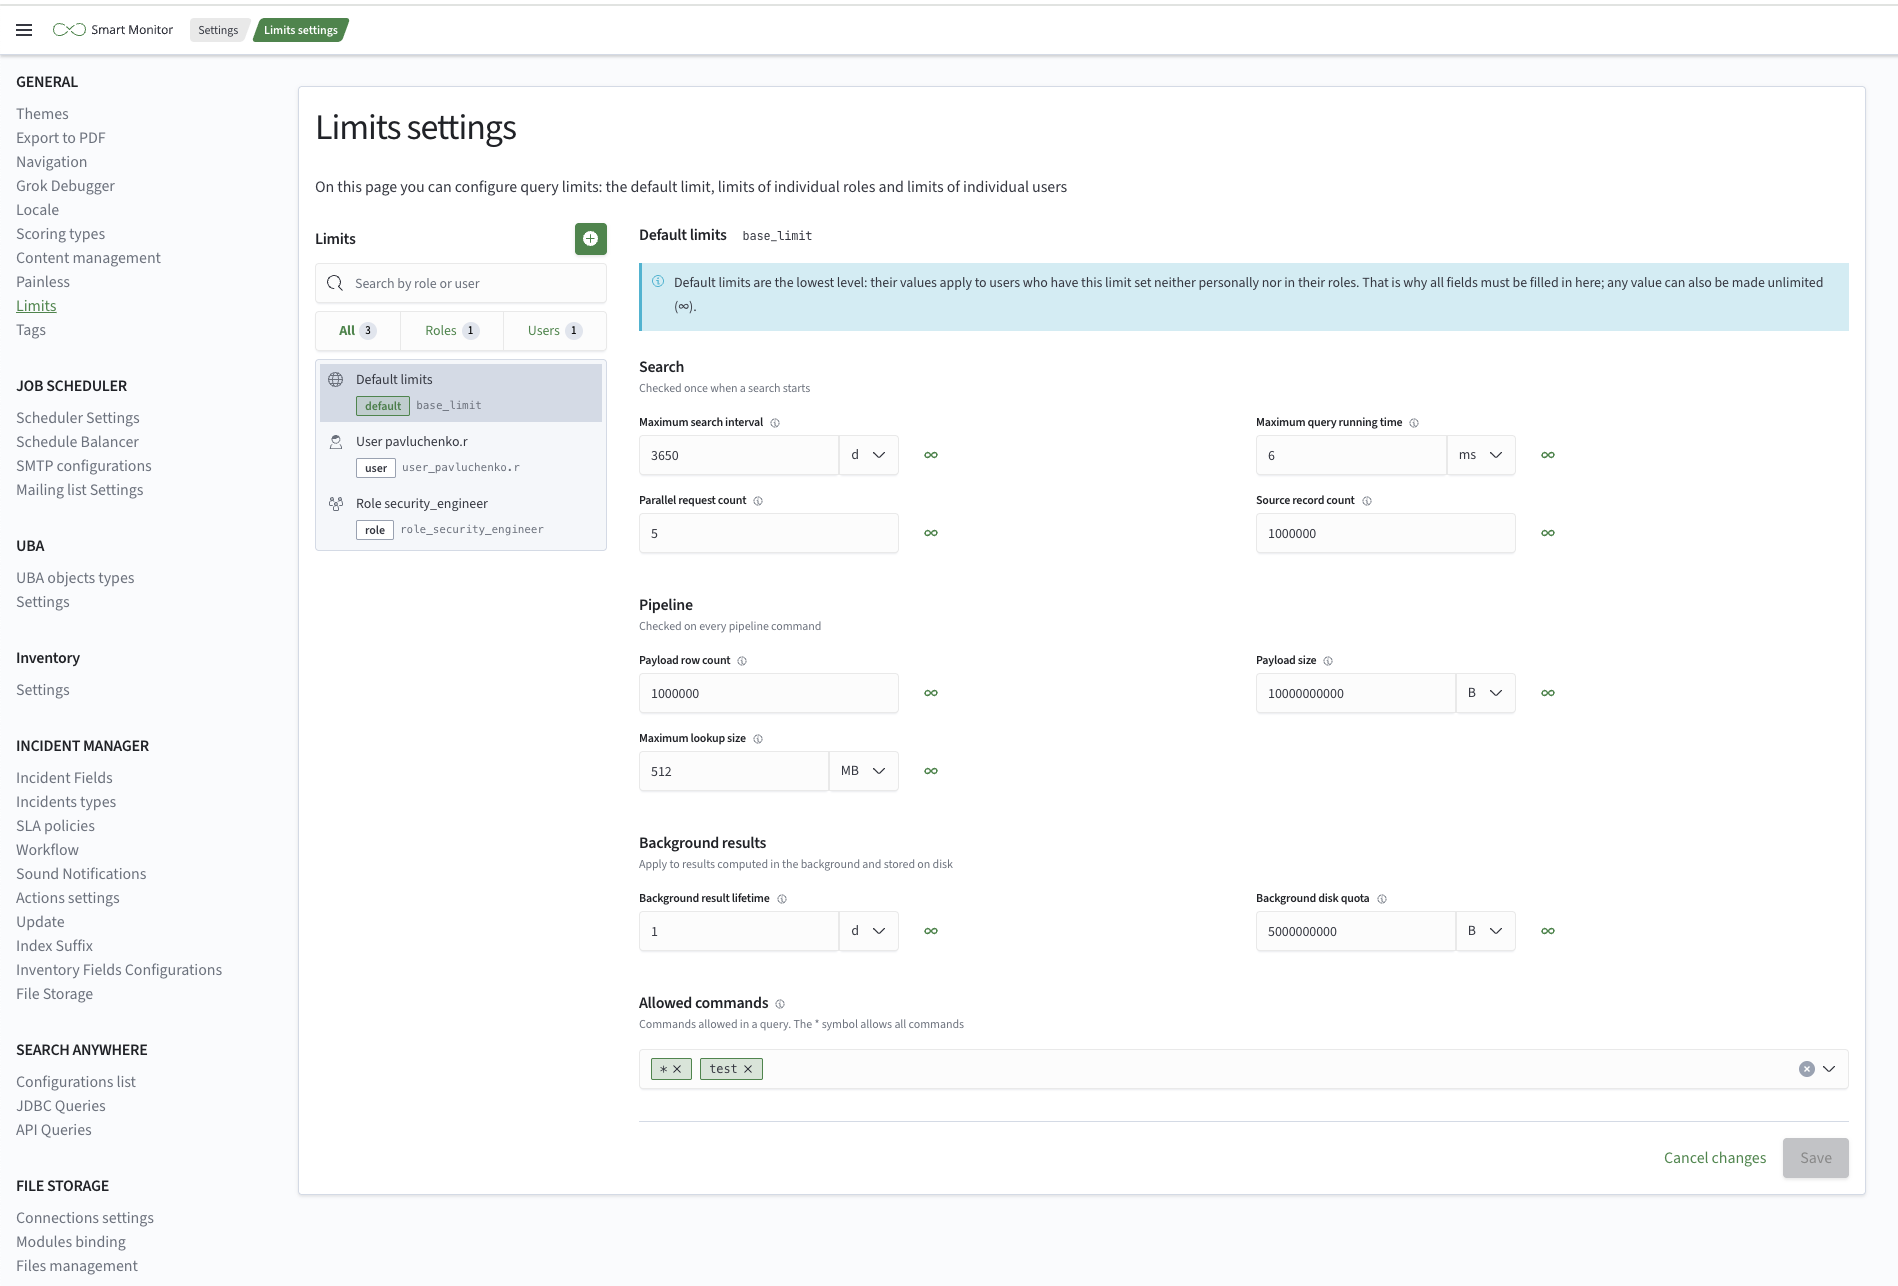
Configuring default limits
- Select the default limits in the configuration list.
- Fill in all numeric fields or select
Unlimited (∞)for the required parameters. - Set the default list of allowed commands. The
*symbol allows all commands. - Click
Save.
Default values are used for inheritance. Changes to a default value apply to roles and users that inherit the corresponding parameter.
Configuring role or user limits
- To create a configuration, select
For a roleorFor a userand choose the role or user. To edit an existing configuration, select it in the list. - Click
Add limitand add the numeric fields to be configured for the role or user. The system applies the inheritance algorithm to the remaining fields. - Enter values and select units. Select
Unlimited (∞)if required. - Specify the allowed commands. A personal user list replaces the inherited list. Role lists are combined without duplicates. The default list follows the same rules as default numeric values.
- Under
Effective limits, check the resulting values and their sources. - Click
Save. The new values apply to subsequent queries, including queries from users who inherit the modified limit.
To restore the saved values, click Cancel changes. If saving fails, the entered values remain in the form for resubmission.
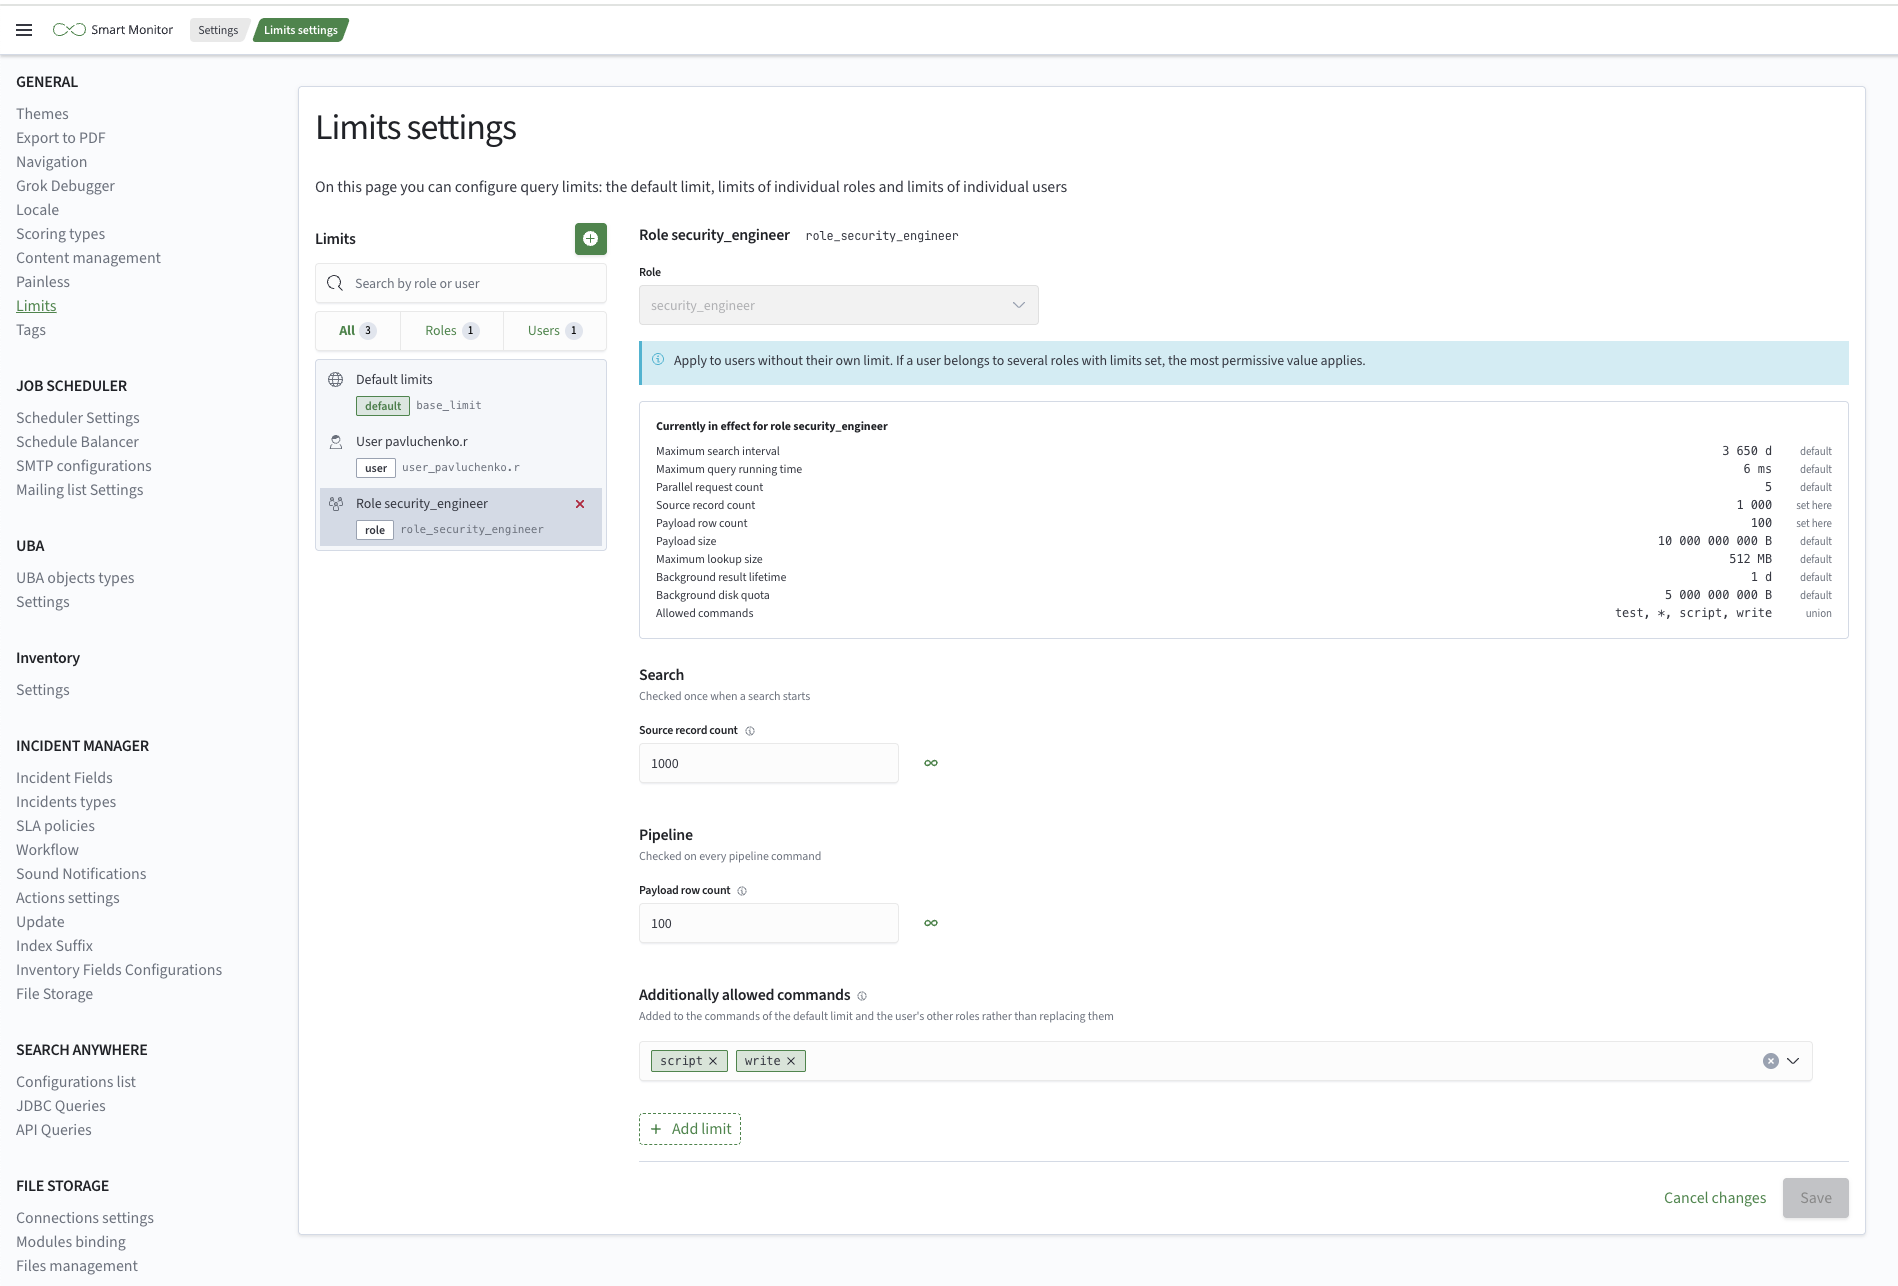
Role configuration example
The following limits are configured for the role security_engineer:
| Name | Value |
|---|---|
max_qsize | 1000 |
max_payload_row_count | 100 |
allowed_commands | scriptwrite |
The effective limits section displays the role’s own and inherited values.
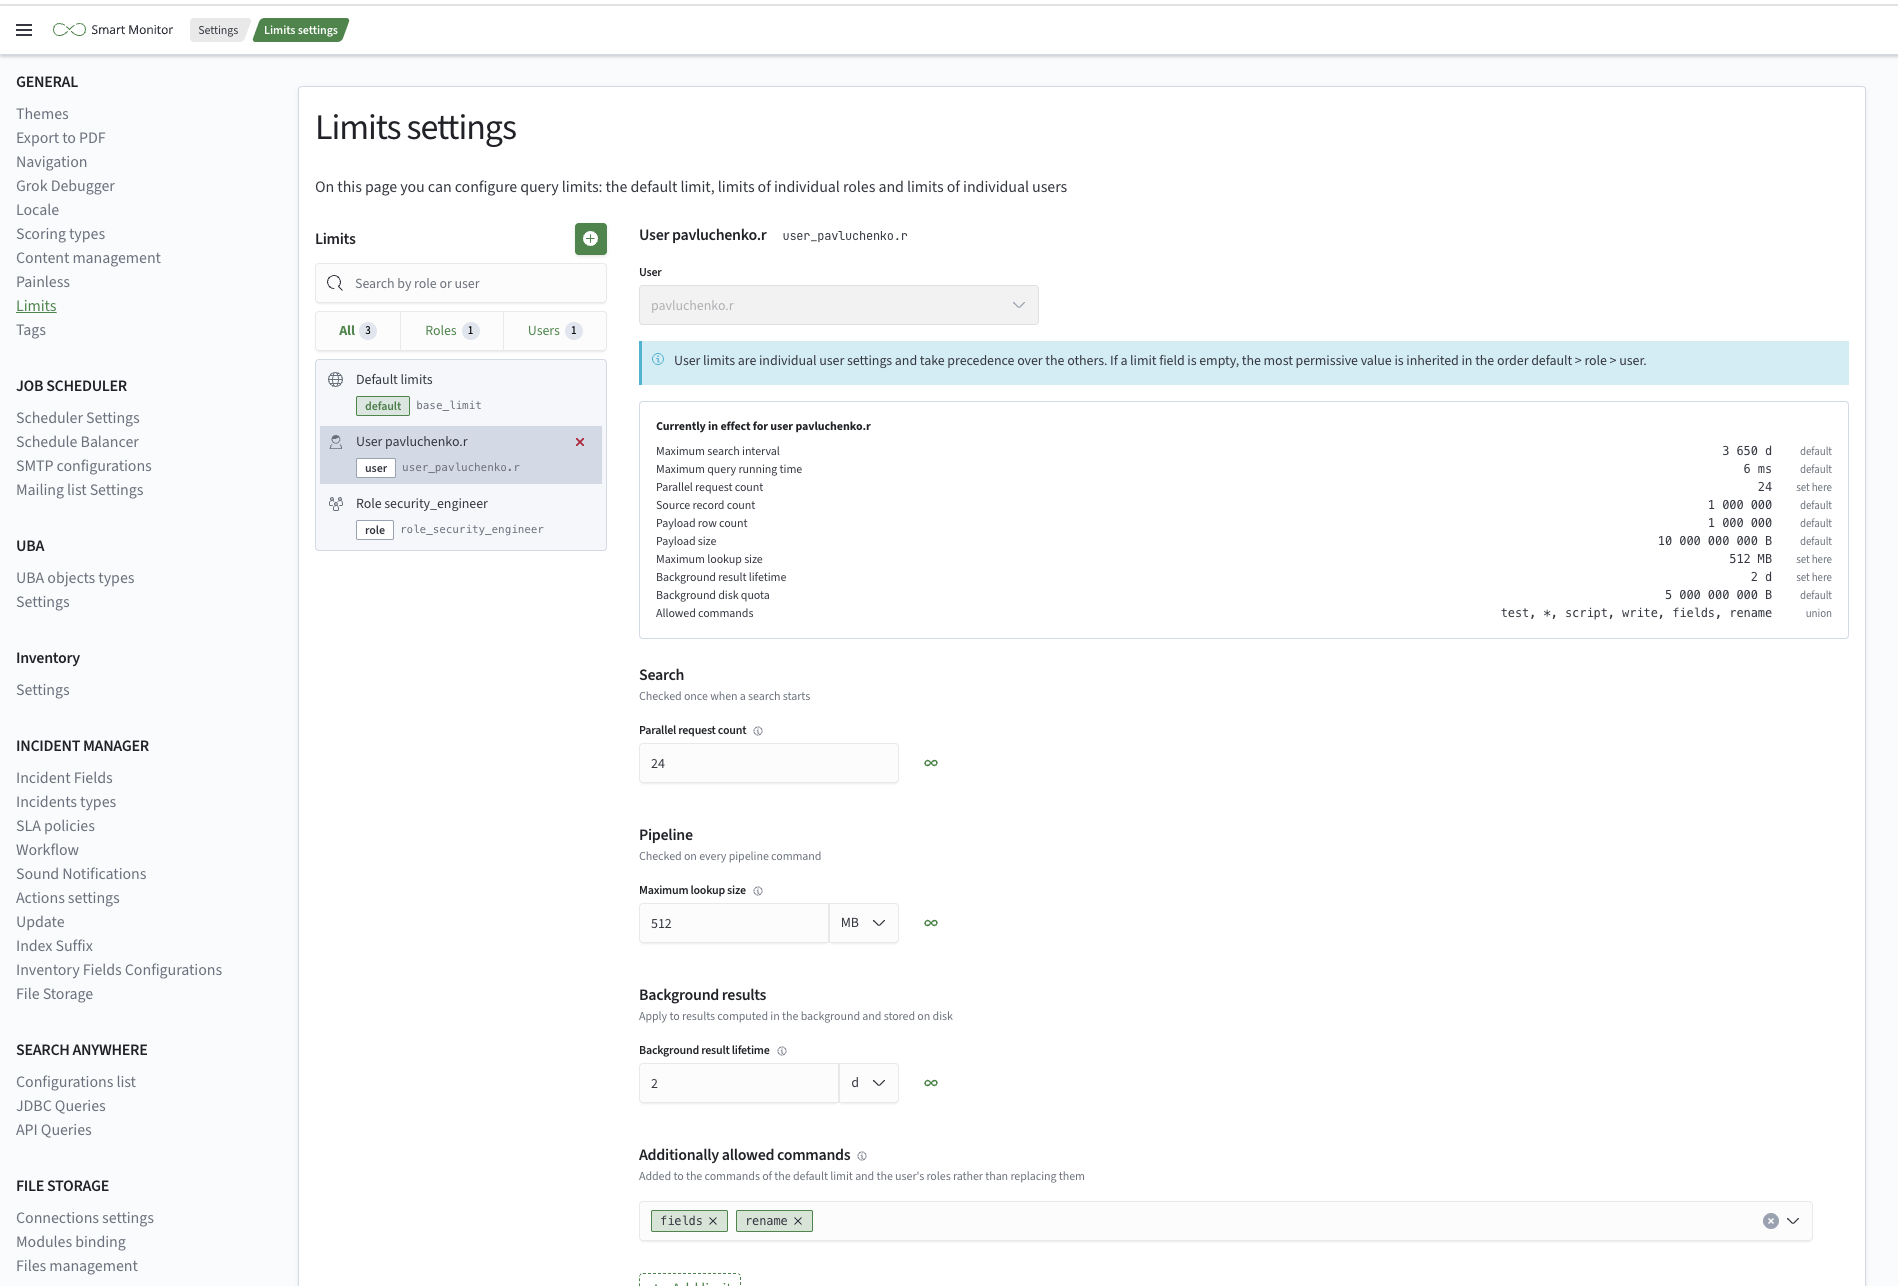
User configuration example
The user pavluchenko.r is assigned the following limits:
| Name | Value |
|---|---|
max_parallel_request_count | 24 |
max_lookup_size | 512 MB |
background_result_ttl | 2 days |
allowed_commands | fieldsrename |
The user's personal command list replaces the inherited lists.
Values and units
To remove a numeric restriction, select Unlimited (∞). The interface submits the value -1 when saving. The value 0 is a numeric restriction and does not mean unlimited.
Select measurement units: seconds, minutes, hours or days for time; bytes, KB, MB, GB or TB for size. When saving, the interface converts time values to seconds and size values to bytes. Size units differ by a factor of 1024: 1 KB = 1024 bytes.
Deleting a limit field or configuration
Deleting a limit field
To delete an individual field from a role or user configuration, click the delete button next to the field, then click Save.
After a field is deleted, the system determines its value using the inheritance algorithm. For a user, the system considers role configurations. A missing field in an existing role configuration uses the default value. Roles without a limit configuration are excluded from the calculation. If no applicable values are available, the default limit applies.
Deleting a role or user configuration
To delete an entire configuration, click the delete button next to the role or user in the configuration list and confirm the action. The system deletes all fields in the configuration and determines the effective values again through inheritance. The role or user account is retained.
Limit inheritance
The system determines each field’s value separately:
- It checks the user’s personal configuration. If the field is set, its value replaces the inherited value.
- If the personal value is absent, it considers the user’s roles. For each role with a limit configuration, it uses the field value or, if absent, the default value. Roles without a limit configuration are excluded from the calculation.
- It selects the largest value. If any value is
Unlimited (∞), it removes the restriction. - If no personal or role value is available, it applies the default limit.
The resulting values and their sources are displayed under Effective limits.
Allowed command inheritance
The same inheritance order applies to allowed_commands. A personal user list replaces inherited lists. If no personal list is set, the system combines role lists without duplicates. Unlike numeric parameters, command lists do not use a maximum value.
The default list applies when an existing role configuration lacks allowed_commands, or when no list is available from the user or applicable roles. Otherwise, the default list does not participate in the calculation. Roles without a limit configuration are excluded.
The * symbol in the resulting list allows all commands. A personal list without * can replace an inherited list containing *.
Configuration example
The user is assigned the roles developer and user. Both roles have limit configurations. In the table, “Not set” indicates a missing field in an existing role configuration.
| Parameter | Default | Role developer | Role user | User | Resulting value | How the result is selected |
|---|---|---|---|---|---|---|
max_qsize | 2000 | Not set | 1000 | 500 | 500 | The system applies the personal value 500 without comparison with default or role values |
max_dt_interval | 30 days | 7 days | Not set | Not set | 30 days | The field is absent from the configuration of the role user, so the default of 30 days applies. The role developer specifies 7 days. The resulting value is 30 days |
max_search_running_time | 1 minute | 5 minutes | Not set | Not set | 5 minutes | The default of 1 minute applies to the role user. The role developer specifies 5 minutes. The resulting value is 5 minutes |
allowed_commands | source | stats, eval | eval, write | streamstats | streamstats | The personal list replaces inherited lists. If no personal list is set, the role lists are combined into stats, eval, write, without duplicates or the default source |
Deleting the entire configuration for the role user excludes that role from the calculation. The resulting max_dt_interval is 7 days from the role developer; the default of 30 days does not participate in the comparison. If no personal value or applicable role configuration is available, the default limit applies.
Numeric limit inheritance examples
In all three examples, the user has the roles developer and user, and no personal max_dt_interval is set. Interval values are in seconds: 2592000 is 30 days, 604800 is 7 days, and 86400 is 1 day.
1. Both role configurations contain the field
{
  "base_limit": {
    "max_dt_interval": 2592000
  },
  "role_developer": {
    "max_dt_interval": 604800
  },
  "role_user": {
    "max_dt_interval": 86400
  }
}
Both roles specify the field. The system compares 7 days with 1 day and selects 7 days. The default of 30 days does not participate.
2. A role configuration lacks the field
{
  "base_limit": {
    "max_dt_interval": 2592000
  },
  "role_developer": {
    "max_dt_interval": 604800
  },
  "role_user": {
    "max_qsize": 1000
  }
}
The role_user configuration exists but lacks max_dt_interval. The system uses the default of 30 days for this role and compares it with 7 days from role_developer. The result is 30 days.
3. A role has no limit configuration
{
  "base_limit": {
    "max_dt_interval": 2592000
  },
  "role_developer": {
    "max_dt_interval": 604800
  }
}
The role_user configuration is absent, so the role user is excluded from the calculation. The resulting value is 7 days from role_developer. The default of 30 days does not participate.
System limit settings
Global limit settings are in _cluster/settings under sme.core.limits.
The table lists the system settings and their default values. Names are relative to sme.core.limits: for example, the full path for enable_limits is sme.core.limits.enable_limits.
| Name | Description | Default value |
|---|---|---|
enable_limits | Enables or disables limiting | true |
check_base_limit | Creates the limit index and default limit if they are missing | true |
index_name | Sets the index used to store limits | .sm_sme_limits_user |
max_subsearch_hits_count | Limits the number of documents returned by a subquery | 50000 |
list_limit | Limits the number of values returned by the list function of stats | 100 |
sort_limit | Limits the number of documents sorted by sort | 10000 |
Limit parameters
The table lists the units in which the interface saves field values through the API.
| Parameter | Purpose | Storage unit |
|---|---|---|
max_dt_interval | Maximum duration of the search time range | Seconds |
max_search_running_time | Maximum query running time | Seconds |
max_parallel_request_count | Maximum number of parallel queries | Count |
max_qsize | Maximum number of records read from the source | Count |
max_payload_row_count | Maximum number of documents passed between pipeline commands | Count |
max_payload_size | Maximum amount of data passed between pipeline commands | Bytes |
max_lookup_size | Maximum size of lookup data | Bytes |
background_result_ttl | Retention time for background query results | Seconds |
background_disk_quota | Disk quota for background query results | Bytes |
allowed_commands | Allowed SML commands | Array of command names |